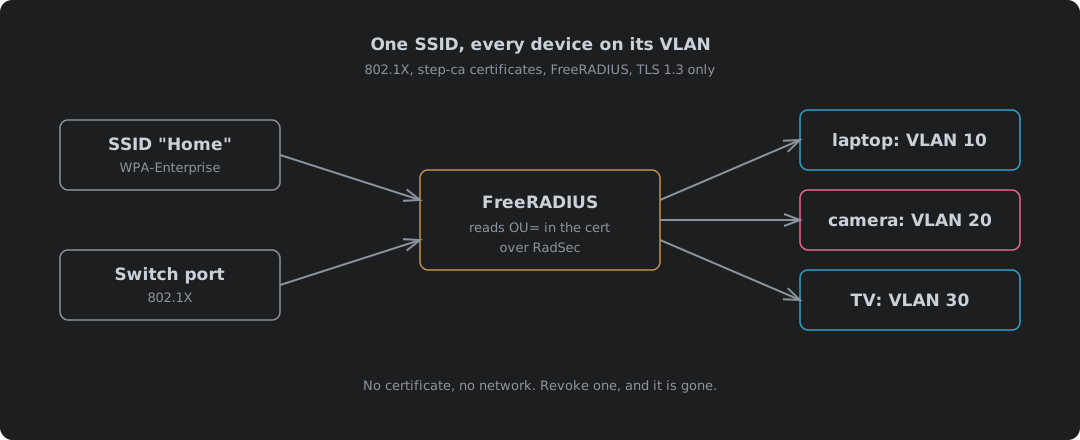
One SSID, Every Device On Its Own VLAN: 802.1X With step-ca Certificates
Certificate-based 802.1X (EAP-TLS) for wired switch ports and a single WPA2/WPA3-Enterprise SSID, where the RADIUS server decides which VLAN each device lands on. step-ca 0.30.2 stamps a role into every device certificate and refuses one without; FreeRADIUS 3.2.10 maps that role to a VLAN, lets a per-device list override it, and runs TLS 1.3 only. Why a shared WiFi password is the problem, why certificates and why TLS 1.3, the revocation trap where FreeRADIUS ignores a new CRL on a HUP, what a device that does not check the server name will trust, protecting the RADIUS traffic itself with Message-Authenticator and RadSec over TLS 1.3, radsecproxy for kit that only speaks UDP, a wired port and a WiFi network simulated end to end, the Netgear and TP-Link settings, the Linux, Apple and Android client settings, every config file in full and as a download, and why so many admins and MSPs still do not bother and Cyber Essentials does not ask them to.