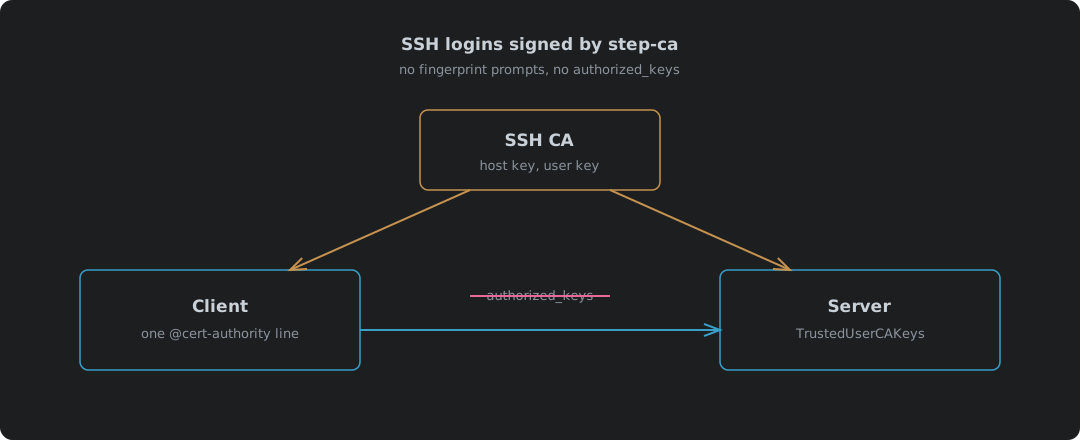
SSH Logins Signed By step-ca: No More authorized_keys
Using step-ca 0.30.2 as an SSH certificate authority, tested with OpenSSH 10.0. Why certificates beat authorized_keys and trust-on-first-use, switching the SSH CA on when step-ca is first set up, signing a host key (and the argument order that trips it), the two sshd_config lines and the single @cert-authority line in known_hosts, a 16-hour user certificate, four login tests including a wrong user and an untrusted host, renewing a host certificate with sshpop, and where it falls down.