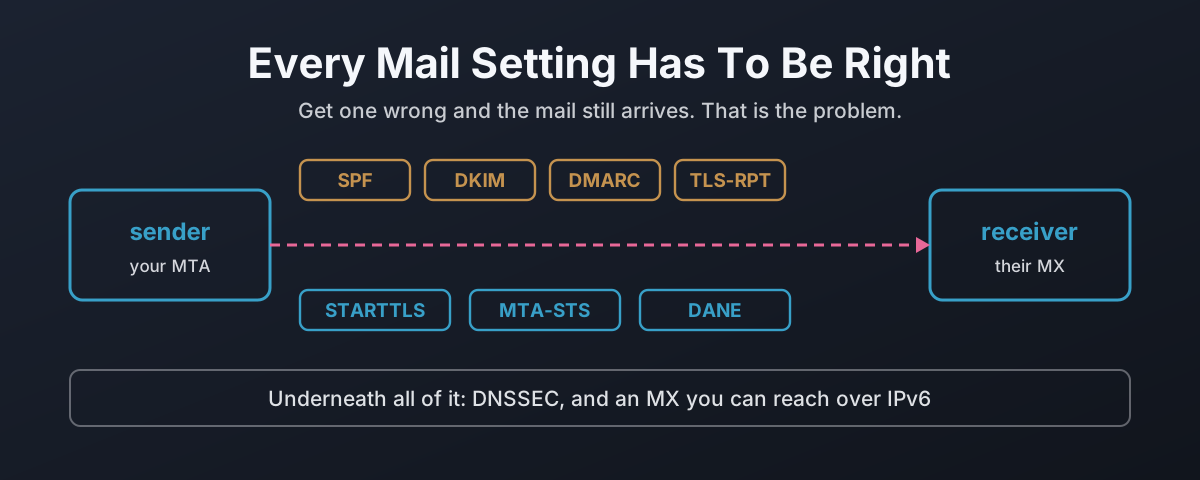
Why Every Mail Setting Has To Be Right
Every layer of email security is designed to fall back to working rather than fail safely. Strip the STARTTLS line out of a greeting and an opportunistic sender carries on in the clear, which RFC 3207 both describes as an attack and, on a public server, forbids you to defend against. This post captures that man-in-the-middle in a lab, then walks the seven settings that protect a message in transit, showing for each one what it protects, what it does not, and how it fails open when it is wrong. From there to DANE: why a TLSA record is worthless without DNSSEC under it, why 3 1 1 and key reuse matter, and how a stale record is the one failure that closes rather than opens. Then a read-only census of UK banks, the big mail providers and the certificate authorities, counting how many actually do any of it.