Skip to content
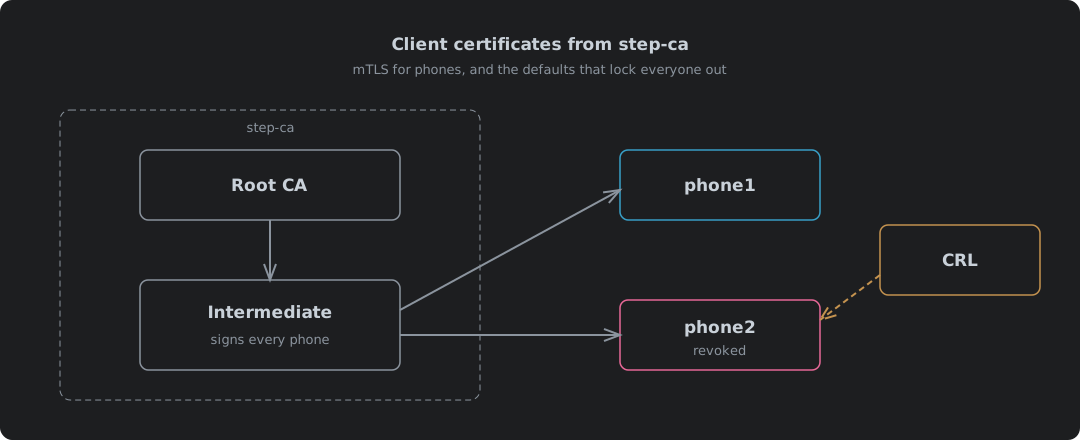
step-ca issuing client certificates to phones from its intermediate, with a CRL marking a lost phone as revoked

Client Certificates From step-ca, And The Defaults That Lock Everyone Out

Using step-ca 0.30.2 to issue client certificates for mutual TLS, tested end to end with nginx 1.30.5 and Caddy 2.11.7. Why phones are the hard case, raising the 24-hour certificate limit in ca.json, turning the CRL on, why it fails with “different CRL scope” until idpURL and a template add a matching distribution point, the root CRL nginx needs for the whole chain, publishing CRLs over plain HTTP on IPv4 and IPv6, the refresh job that stops an expired CRL locking everyone out, and issuing, packaging, installing and revoking a phone’s certificate.
9th October 2026 · 11 min · 2464 words · Damien Dye
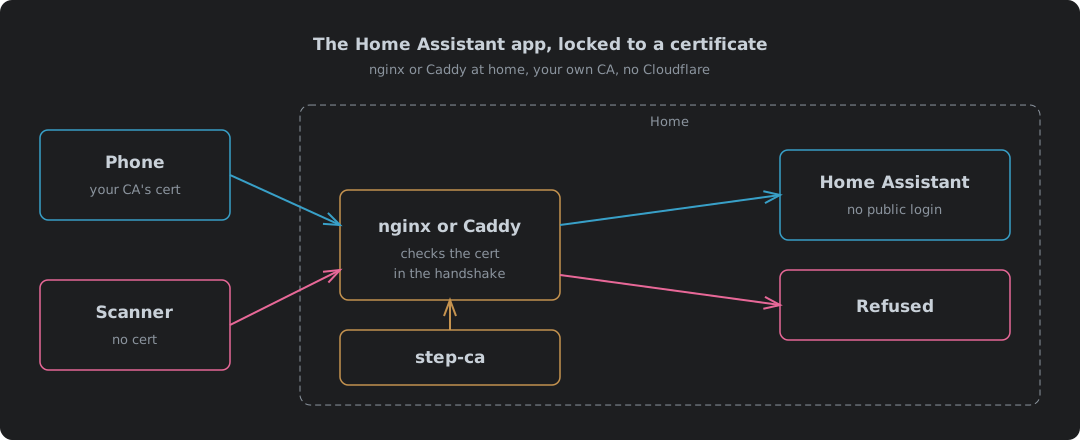
A phone holding a certificate from your own CA passes nginx or Caddy at home and reaches Home Assistant, while a scanner without one is refused in the handshake

The Home Assistant App Locked To A Certificate, With nginx Or Caddy And No Cloudflare

Locking the Home Assistant app to a client certificate with nginx or Caddy at home, with step-ca as the certificate authority instead of Cloudflare. What changes when Cloudflare leaves the path, an nginx config and a Caddy config each tested with no certificate, a good one, a revoked one and a WebSocket upgrade over IPv4 and IPv6, why nginx can check a CRL and Caddy can only keep an allowlist, the Home Assistant trusted-proxy settings, what the phone needs installed, and where it falls down.

9th October 2026 · 10 min · 2145 words · Damien Dye