Skip to content
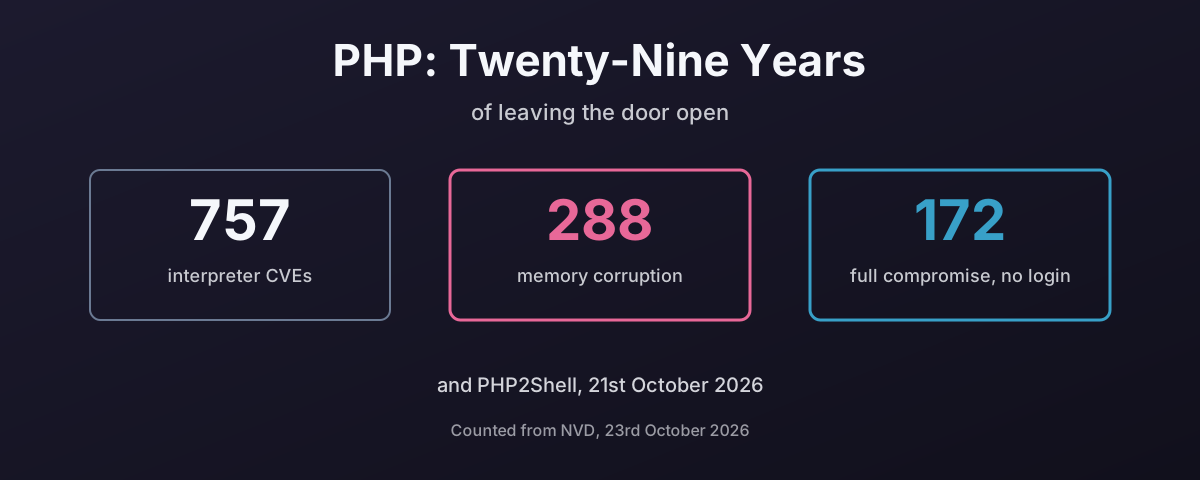
757 PHP interpreter CVEs since 1997, at least 288 memory corruption, 172 rated full remote compromise without a login

PHP: Twenty-Nine Years Of Leaving The Door Open

PHP2Shell, disclosed on 21st October 2026, is unauthenticated remote code execution in the PHP interpreter itself, every version back to 5.4, exploited before the patch existed. It is the latest entry in a long record: 757 CVEs against the interpreter since 1997, at least 288 of them memory corruption and 172 rated as full remote compromise without a login. This post counts that record from NVD and the CISA KEV catalogue, explains why a C engine and a language that took a decade to remove register_globals make the same mistake twice, looks at what WordPress does to the numbers, how web shells stay put and how to stop them, the two times php.net itself was broken into, the share of the web still running versions nobody patches, and why the usual deployment, one process holding the templates, the logic, the SQL and the database password, turns every one of those bugs into everything. And why, having given up on PHP myself, I think you should look at leaving it for a memory-safe language such as Go.

23rd October 2026 · 29 min · 8074 words · Damien Dye

Sorting TSC When Your Firmware Is Broken

On every boot for four months my ThinkPad E595 handed Linux one CPU core three seconds behind the other seven, and the kernel dropped the TSC for HPET. What the warning means, why an AMD Zen machine has no way to repair it from inside Linux, what 40 boots of journal say about the firmware, why tsc=reliable is the wrong answer, and how tscsync measures and moves the counters in UEFI before the kernel ever sees them, including the one core it marked BAD that Linux accepted anyway. Updated for BIOS 1.30: it does not fix the offset, and the kernel’s clocksource watchdog dropped the TSC on two boots even after tscsync synced the cores. With tsc=nowatchdog it held, and a five-minute check against the real-time clock, source included, found no warps and no drift. Last, what the fallback does on any KVM hypervisor, Proxmox or not: the master clock goes, guests lose their fast clock read, and on this laptop a guest clock read came out seven times slower.

11th October 2026 · 23 min · 5100 words · Damien Dye

My YubiKey Logs Me In. My Keyring Never Got Told.

Log in with a YubiKey and GNOME asks for a password anyway, because the login keyring is encrypted with a password your login never produced. This post covers why pam_u2f being sufficient starves the keyring, what the usual fixes cost (blank password, typing it anyway, the TPM), and the fix I built: the key’s FIDO2 hmac-secret, gated on PIN and touch, decrypting a stored copy of the account password and unlocking oo7-daemon at login. Then what the build turned up: Fedora 45 had swapped gnome-keyring for oo7, oo7’s placeholder keyring takes the first password you type as its own, the FIDO2 tools only read a PIN from a terminal, and a reset script that would have left me with no keyring at all, caught by testing it against a throwaway daemon first. The scripts, an installer and that test harness are available to download.

7th October 2026 · 12 min · 2567 words · Damien Dye

Webex Is Looking For Your Certificates On A Cisco Build Server

Webex 46.8.0.35631 on Fedora 44 sits behind a yellow banner reading “Offline - No internet connection” while every other program on the machine reaches the internet without complaint. It stopped the VoIP line dead. The network was never the problem: Cisco bundle their own fork of OpenSSL and built it with OPENSSLDIR set to /workspace/.conan2/p/b/cisco8ee8b59cf93de/p/ssl, a directory that exists on a build container and nowhere else, so it loads no trust anchors and every handshake fails. The post runs in order: what the broken state actually is, asking the shipped library where it thinks its certificates live, reproducing the exact error code outside Webex, why nothing warns you, the two fixes that do not work and why, and the one that does. Then the build process: they used $ORIGIN for the code and left three data paths absolute, the RPM header names a container ID so the container was already in the pipeline and never used to run the result, the package requires a glibc from 2018 because they will not link statically, 2.2 GB is shipped twice, and it carries no documentation and no file marked as configuration. Then how it should have been built, the six fixes and the one-line check that catches it. And finally the cross-check: Cisco hold 98 entries in CISA’s known-exploited catalogue, second only to Microsoft, and a trust path nobody checked and a bypass nobody checked are the same failure at different stakes.

15th September 2026 · 42 min · 9141 words · Damien Dye

A VPN Out of Parts: PPP, Tap Devices and Netcat

A VPN is two jobs: something that makes a virtual link, and something that carries the bytes. PPP has done the first since 1994 and does not care what the second is — which is why PPTP, L2TP and every dial-up line you ever used are the same protocol over different carriers. Netcat is a carrier. This builds it both ways. First pppd: the pty option and what it does with a pseudo-terminal, the TCP version everyone tries first, why running a stream protocol inside TCP melts under loss, the UDP version that is the one to use, the async HDLC framing and the ACCM that decides how much bandwidth goes on escaping control characters, addressing and routing and IPV6CP, and keeping the link up when the carrier dies without telling you. Then the same tunnel with no PPP at all — a tap device, one datagram per frame over UDP, the length prefix you have to invent yourself over TCP, tun against tap, and bridging. Then the part netcat has no answer for: wrapping the carrier in TLS with ncat, stunnel and openssl, and in DTLS with socat, which is the shape you actually want. It is never really the right tool, and that is the point: it shows how egress behaves once an attacker has root inside your network and outbound access was not blocked by default, and why default-deny at the border is the only control that was ever real.

14th September 2026 · 60 min · 13157 words · Damien Dye

Ping: The Diagnostic Tool That Opens a Whole Lot More

Ping, not the rest of ICMP, is the liability: echo is a channel every host must answer with your own bytes, so a network that ‘only allows ping’ already has a full VPN out. This walks the threat first — what it costs your egress, and how a visitor on your WiFi or an unlocked ethernet port can open one — then three working tunnels built on ping alone (Hans, icmptunnel, and a short Python one with AES-128), the MTU and IPv6 catches, and the rule that shuts it: drop echo, keep the errors, in nftables, pf, Cisco, Junos, MikroTik and Windows.

1st September 2026 · 36 min · 7657 words · Damien Dye

The Firewall Is Eleven Hops Away

“Port 445 is blocked somewhere” is not a diagnosis, and it is why firewall tickets bounce between you and your provider for a week. Every router on the path owes you an ICMP Time Exceeded when your hop budget runs out, and that turns a timeout into a distance. I walked the TTL up on my own line and found three faults I did not know I had: an SMB drop eleven hops out, forged SMTP resets one hop away, and an IPv4 rule with no IPv6 twin.

28th August 2026 · 38 min · 8038 words · Damien Dye