Skip to content
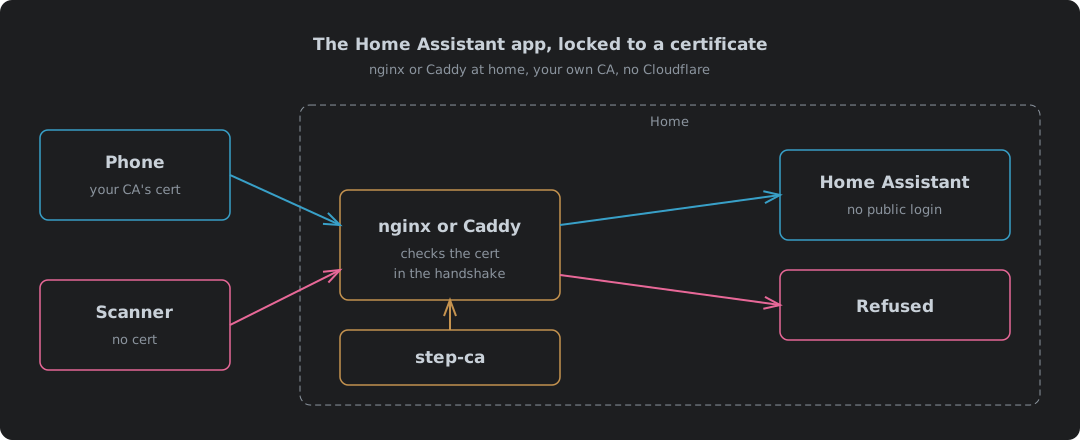
A phone holding a certificate from your own CA passes nginx or Caddy at home and reaches Home Assistant, while a scanner without one is refused in the handshake

The Home Assistant App Locked To A Certificate, With nginx Or Caddy And No Cloudflare

Locking the Home Assistant app to a client certificate with nginx or Caddy at home, with step-ca as the certificate authority instead of Cloudflare. What changes when Cloudflare leaves the path, an nginx config and a Caddy config each tested with no certificate, a good one, a revoked one and a WebSocket upgrade over IPv4 and IPv6, why nginx can check a CRL and Caddy can only keep an allowlist, the Home Assistant trusted-proxy settings, what the phone needs installed, and where it falls down.
9th October 2026 Β· 10 min Β· 2145 words Β· Damien Dye
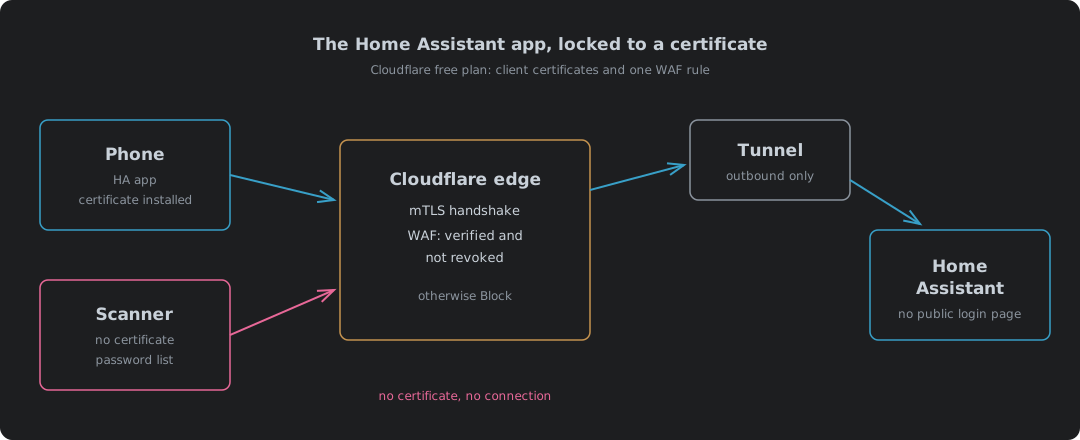
A phone holding a client certificate passes Cloudflare's edge check and reaches Home Assistant through a tunnel, while a scanner without one is blocked at the edge

The Home Assistant App Over Cloudflare, Locked To A Certificate, On The Free Plan

Reaching Home Assistant from the Android app away from home without putting a login page on the internet. How the remote-access options compare on exposure, real cost (machine load and DDoS as well as the bill), blocking risk and battery, why Cloudflare Access and service tokens do not suit the app, how the free-plan client certificates and a WAF custom rule lock a tunnel hostname to the phones that hold a certificate, which Home Assistant settings the reverse proxy needs (trusted proxies, IP banning, external URL, connection security level), building the PKCS12 file, and where it falls down. A self-hosted nginx or Caddy version is a separate post.

9th October 2026 Β· 15 min Β· 3688 words Β· Damien Dye