Skip to content
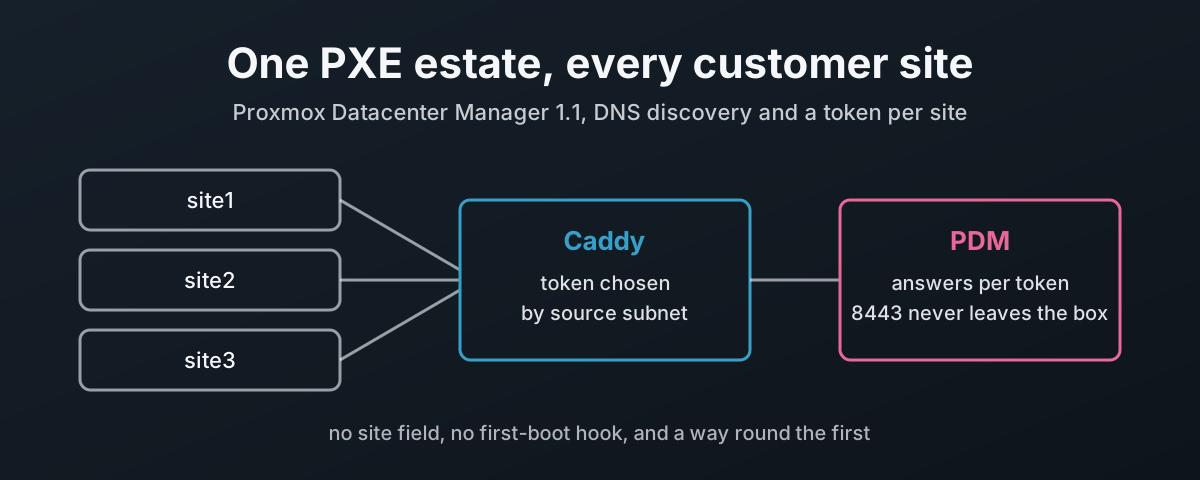
Three customer sites feeding one Caddy, which hands each its own token, in front of one Proxmox Datacenter Manager

One PXE Estate for Every Customer: Unattended Installs with Proxmox Datacenter Manager

Proxmox Datacenter Manager 1.1 can serve answer files to the Proxmox automated installer, which makes it a natural install server for an MSP looking after many customer sites. The use case is a customer who wanted every site built with its own naming, root password and SSH keys, by plugging a server into the right VLAN and booting it, with no serial numbers to collect and no answer file per machine; this post covers that booting and installing half, and leaves joining the cluster aside. It cannot match an answer on the site, and it cannot give a node a first-boot script, and both are shown from PDM’s own source. This builds one PXE estate for every site anyway: one boot image carrying a non-secret catch token, DNS TXT discovery so the image holds no URL, and a Caddy proxy that swaps the catch token for the site’s own bearer token by source subnet. It covers how PDM picks an answer, prepare-iso for iPXE, the DNS records, dnsmasq and the iPXE loop, a hardened Caddy that serves the whole PDM UI on 443 with 8443 closed by nftables, logging which token was used by name only, the post-installation webhook, adding Proxmox Backup Server, and the trade-offs that remain.
7th November 2026 · 35 min · 8070 words · Damien Dye
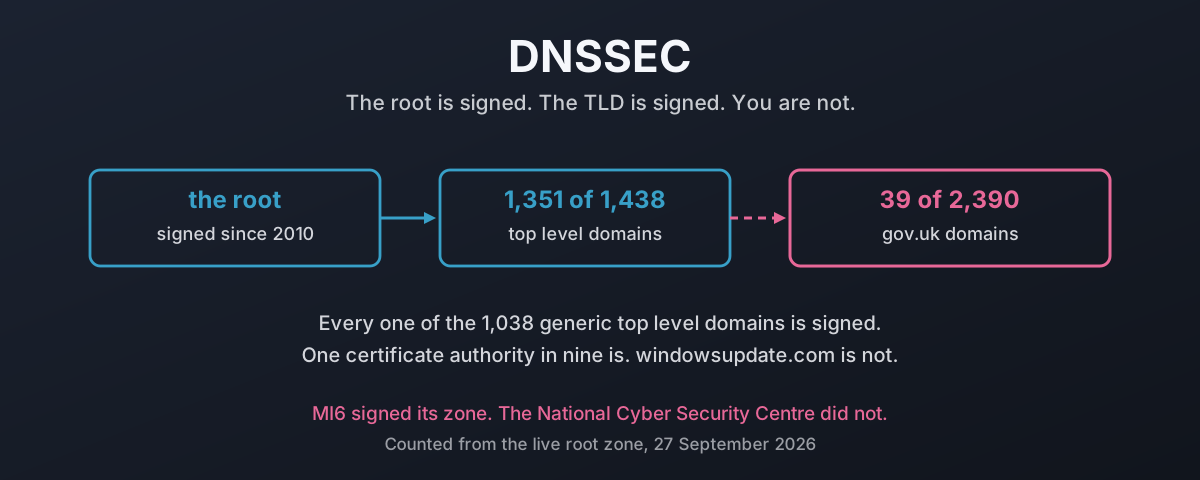
A chain of trust running from the signed root through a signed TLD and stopping at an unsigned second-level domain, with the counted figures beside each step

DNSSEC: Protecting Your Traffic From Forgery

The hard part of DNSSEC was finished years ago. Counted from the live root zone on 27th September 2026, 1,351 of 1,438 top level domains carry a DS record and every one of the 1,038 gTLDs is signed. Then it stops dead. A census of every gov.uk domain in the official register finds 39 signed out of 2,390 that still resolve, nine of them parish councils, while HMRC, the NHS, GCHQ and the National Cyber Security Centre are not among them. One certificate authority in nine has signed. So has one Linux or BSD distribution in five. windowsupdate.com has no DS at all. This is what a forged answer actually costs, what signing does about it, why the usual excuses do not survive contact with the numbers, and whether forty-two years after Mockapetris the real problem is that almost nobody understands what DNS actually promises.

27th September 2026 · 48 min · 10979 words · Damien Dye
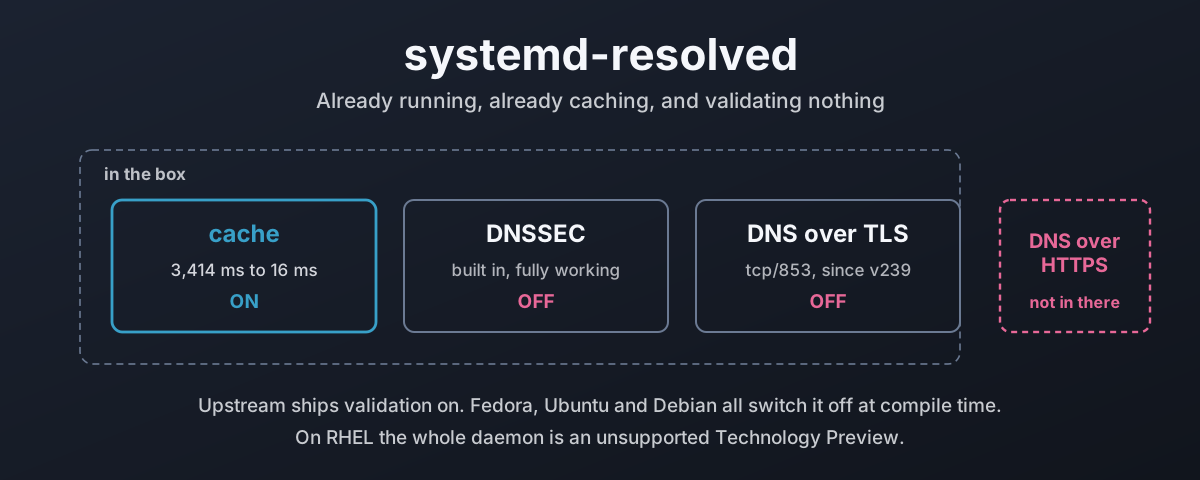
A name lookup passing through systemd-resolved's stub listener into a cache, a validator and an encrypted transport, with the validator and the encryption switched off

Resolved: The Resolver You Are Already Running

systemd-resolved is running on most Linux desktops right now, caching every lookup and validating none of them. This walks the resolution path from nss-resolve to the two stub listeners, measures what the cache is worth on a real machine, turns DNSSEC on and shows the three verdicts it can return, and explains why validation is off by default when upstream ships it on. Then a census of how little of the web is actually signed, DNS over TLS and its strict-versus-opportunistic trap, and the DNS over HTTPS support that has been requested since 2018 and still does not exist. Ends with what Fedora, Ubuntu, Debian and the RHEL family each ship, how to wire it into each one, and why the features your distro disabled are defaults rather than missing code.

27th September 2026 · 38 min · 8443 words · Damien Dye

DNS Over HTTPS Walks Straight Past Your Controls

DNS over HTTPS encrypts your lookups, which is good, and sends them to a resolver of the client’s choosing on port 443, which is the problem. Your own resolver never sees the query, so the blocklist it would have failed, the threat feed it would have hit and the log line it would have written all vanish. This post walks the mechanism: why one encrypted web connection among thousands is invisible at the border, who on a machine can pick a resolver you never chose (the OS, the browser, any app, any script on any web page, and malware), and the documented cases, from a page’s own JavaScript querying a public DoH endpoint that allows cross-origin requests, to Godlua and PsiXBot hiding their command channel inside DoH, to the OilRig APT exfiltrating data over it. Then the case that the privacy story is a cover: DNS over TLS already encrypted DNS in 2016, on a port the network operator can still govern, so the only thing DoH adds over it is defeating the admin, which is why the browser vendors who wrote and shipped it, and the advertising firm that runs the biggest public DoH resolver, are the ones who gained. Then the fix, which is not to ban encryption. Run your own DoH and DoT resolver, advertise it with Discovery of Designated Resolvers, refuse port 53, port 853 and known public DoH resolvers at the border, and answer the Firefox canary so the browser stands down. Keep the encryption. Take back who chooses the resolver. It closes on the fallout: the same DNS-based enforcement runs across Europe and in Australia, and courts in Italy, France, Belgium and Germany are now ordering the public resolvers themselves to block, with Cloudflare fined and appealing, Google refusing in silence and OpenDNS switching itself off for whole countries. The pattern underneath is a US design imposed on the world, and a US government that casts other countries’ laws as extortion of American firms and warns them not to comply.

24th September 2026 · 38 min · 9604 words · Damien Dye

Who Actually Controls DNS

The root of the internet is a 1.5 MB text file that one American company edits and signs. Who really controls DNS, what the 2016 IANA transition did and did not change, and the documented record of how ICANN has used that control.

25th August 2026 · 50 min · 10443 words · Damien Dye

What Happened at Nominet

The .uk registry is owned by its members, and in March 2021 they voted half the board out. What the estate actually looked like from inside, why running .uk alongside dozens of gTLDs shaped how it was run, and how a registry with no regulator ended up disciplined by the only people who could.

25th August 2026 · 29 min · 6147 words · Damien Dye
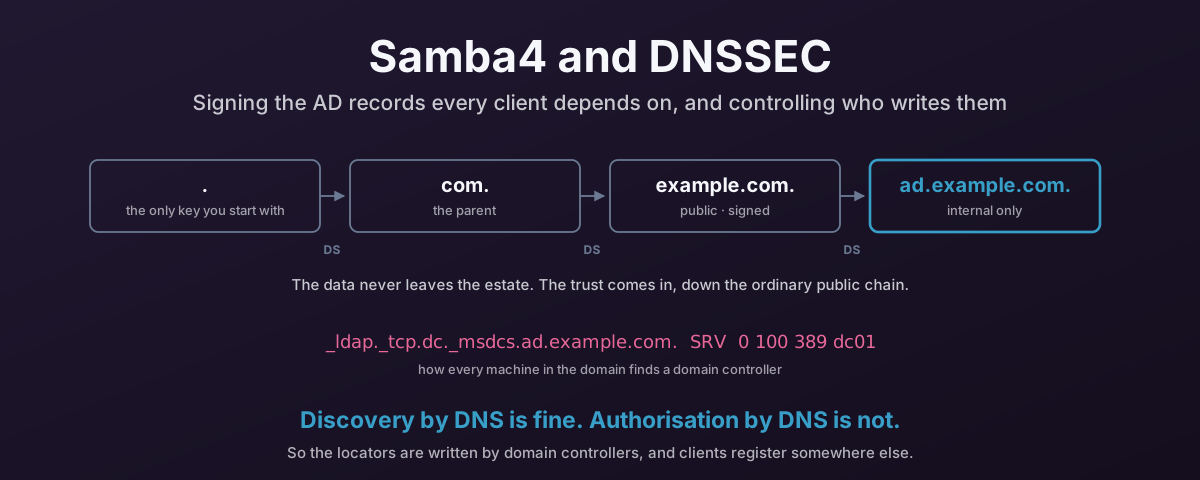
A delegation chain from the root down to an internal Active Directory zone, with client writes confined to a separate sub-zone

Samba4 and Securing AD Records Using DNSSEC

Every domain-joined machine finds its domain controller by asking DNS for an SRV record, so the _msdcs locators are the most security-critical records you own. This is how to publish and sign them properly from a Samba4 DC: BIND with dlz_bind9 reading the directory, inline signing, a hidden primary that clients never reach, and client dynamic updates kept out of the zone that holds the locators. Then how to force Windows and Linux clients to actually check the signatures, because a signed zone nobody validates behaves exactly like an unsigned one.

24th August 2026 · 65 min · 13681 words · Damien Dye