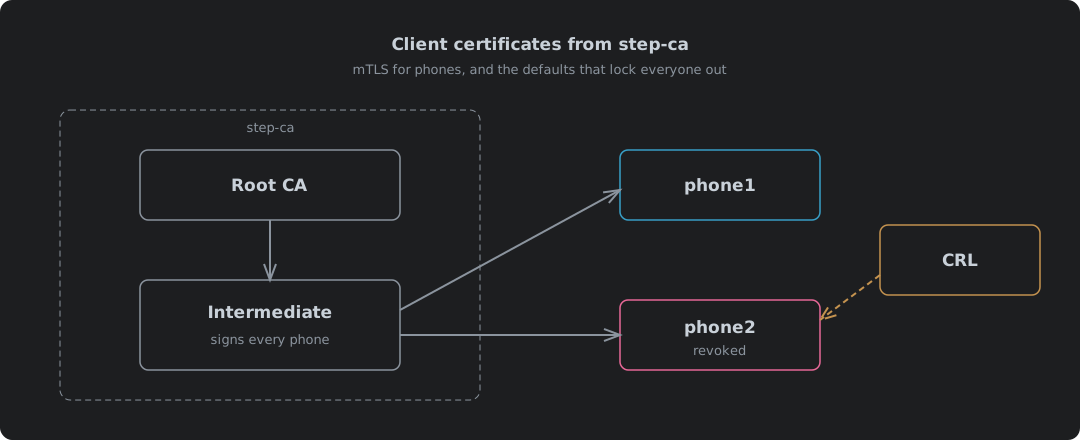
Client Certificates From step-ca, And The Defaults That Lock Everyone Out
Using step-ca 0.30.2 to issue client certificates for mutual TLS, tested end to end with nginx 1.30.5 and Caddy 2.11.7. Why phones are the hard case, raising the 24-hour certificate limit in ca.json, turning the CRL on, why it fails with “different CRL scope” until idpURL and a template add a matching distribution point, the root CRL nginx needs for the whole chain, publishing CRLs over plain HTTP on IPv4 and IPv6, the refresh job that stops an expired CRL locking everyone out, and issuing, packaging, installing and revoking a phone’s certificate.