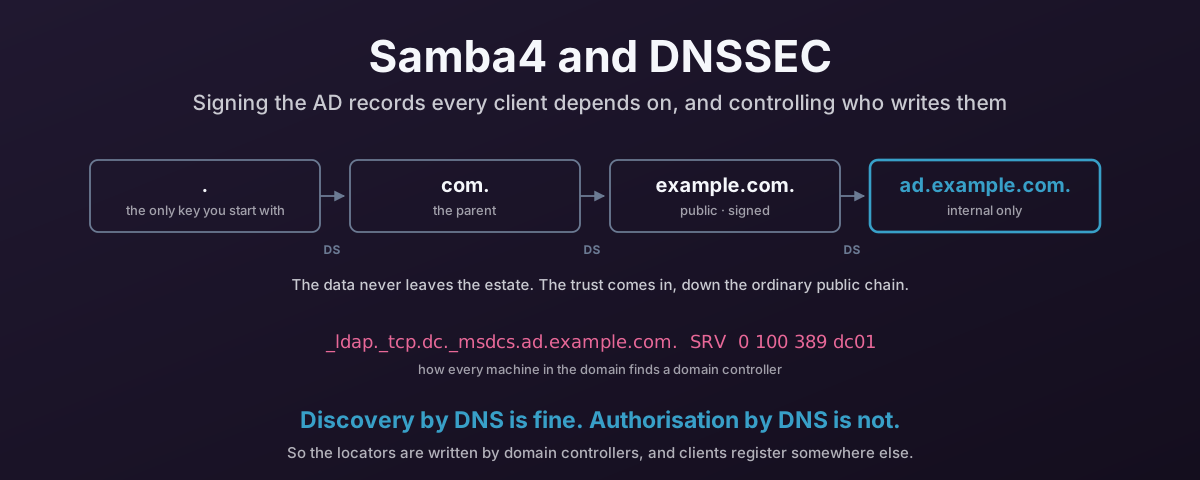
Samba4 and Securing AD Records Using DNSSEC
Every domain-joined machine finds its domain controller by asking DNS for an SRV record, so the _msdcs locators are the most security-critical records you own. This is how to publish and sign them properly from a Samba4 DC: BIND with dlz_bind9 reading the directory, inline signing, a hidden primary that clients never reach, and client dynamic updates kept out of the zone that holds the locators. Then how to force Windows and Linux clients to actually check the signatures, because a signed zone nobody validates behaves exactly like an unsigned one.