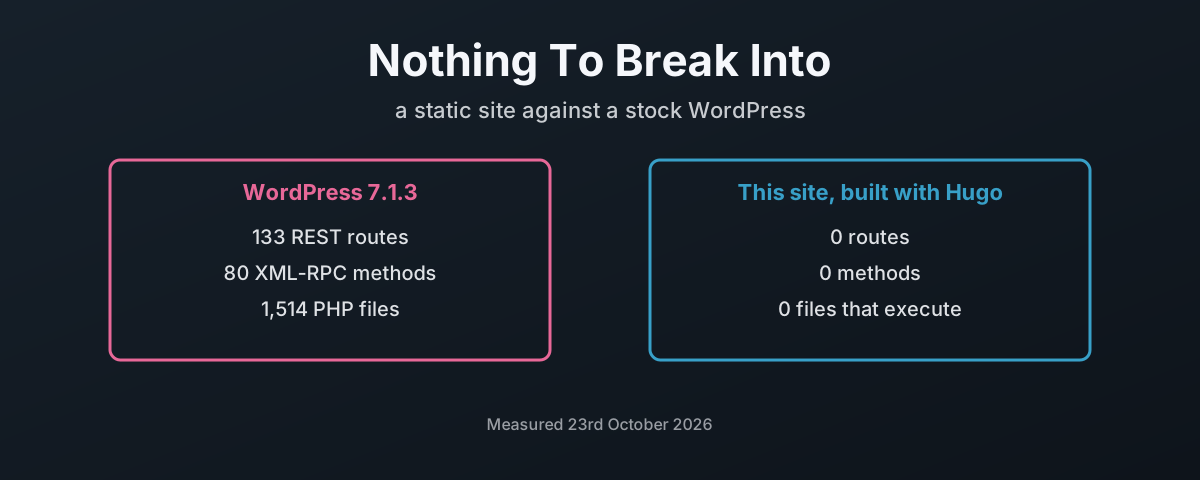
A Static Site Has Nothing To Break Into
This blog is built with Hugo and served as 6,343 plain files, with no code of mine running on any request. Against it, a stock WordPress 7.1.3 measured in a podman lab: 133 REST routes, 62 of them accepting writes, 80 XML-RPC methods, 1,514 PHP files, every one of its 3,785 files writable by the web server’s own user, and a database account holding every privilege. This post counts both attack surfaces, explains what Hugo’s own security model does at build time, owns up to where the risk moves once nothing runs at serve time, including two gaps in how this site was built, one of them now fixed, and sets out how to build a static site offline, once, and upload nothing but the finished files.