DNS is the system that turns a name you can remember into an address a computer can connect to.
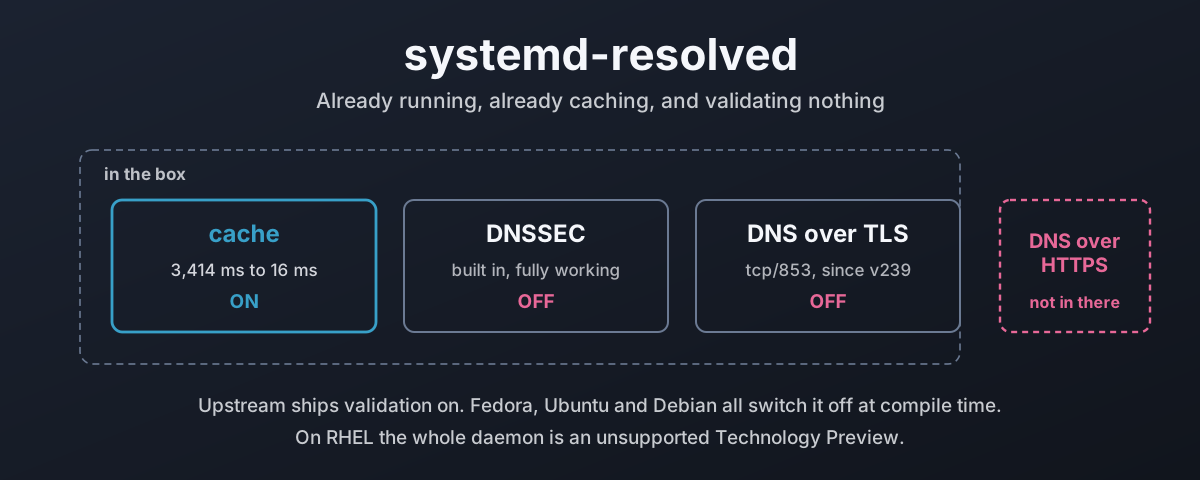
This section is about how that actually works, and how to run it safely.
Every lookup starts at the root of the tree and walks down. Each step hands you the address of the next server to ask. Nothing in the chain is guessed, and nothing is built in except the very first step.
These posts cover:
- How a name is resolved, one delegation at a time.
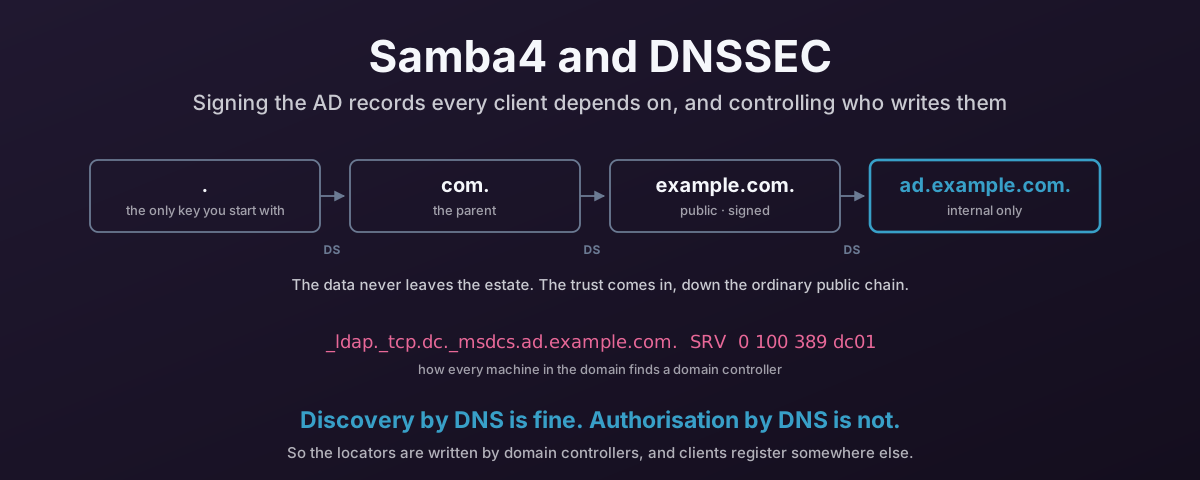
- How services publish where they live, using SRV records.
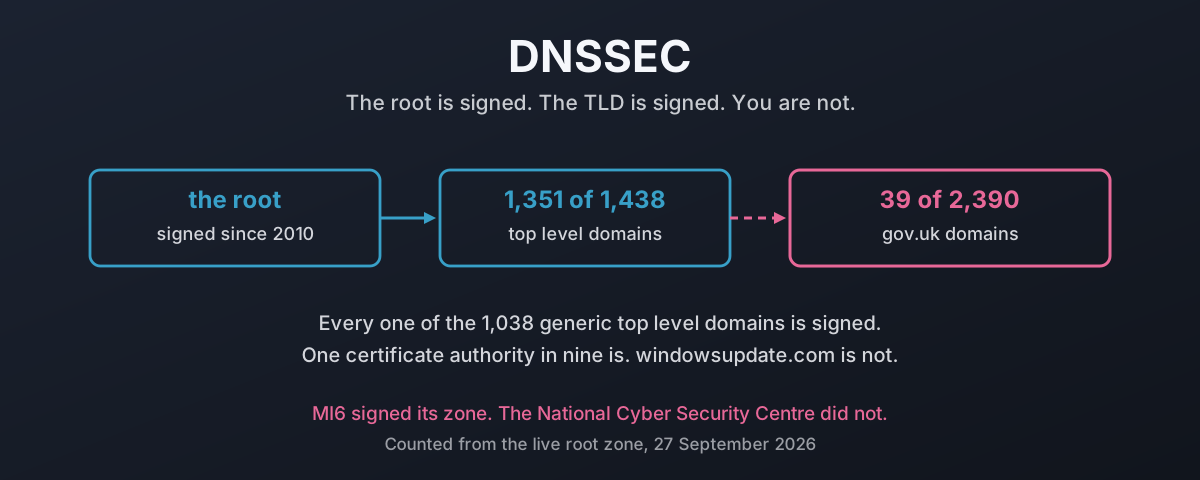
- Why signing your zones matters, and what signing does and does not protect.
- How to publish the DNS for an Active Directory domain from a Samba domain controller, without letting clients write the records they depend on.
- Who controls the root of the DNS, and what the 2016 handover did and did not change.
- How the
.ukregistry is run, and what happened when its own members voted the board out.
The Active Directory posts assume Samba as the domain controller and BIND as the DNS server. The ideas apply to a Microsoft domain controller too.