Guides and notes on TLS certificates — certificate authorities, ACME, Let’s Encrypt and renewals.
A TLS certificate is a small file that proves a website or server really is who it says it is, and lets your connection to it be encrypted so others cannot read the traffic. TLS is the technology behind the padlock in your browser.
These posts cover working with TLS certificates day to day: how the trust chain fits together, running your own certificate authority, using ACME and Let’s Encrypt to get certificates for free, renewing them automatically, and fixing common certificate errors.
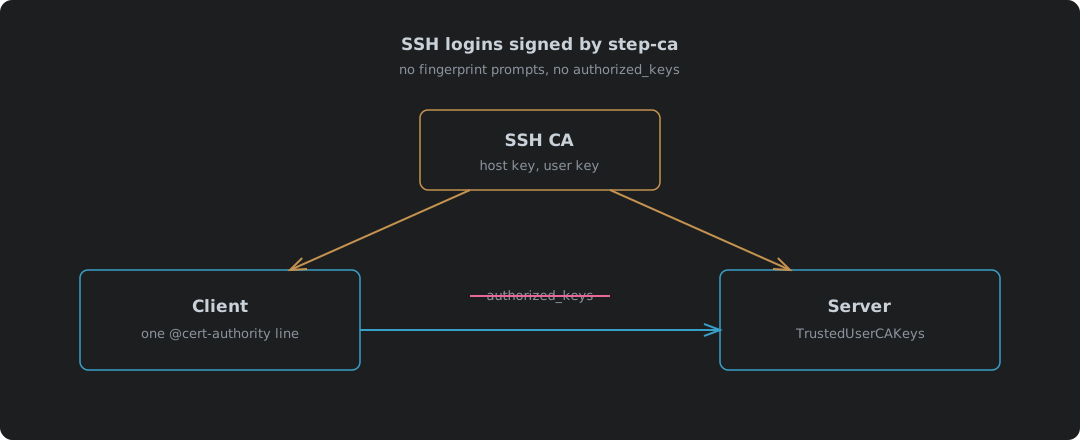
SSH Logins Signed By step-ca: No More authorized_keys
Using step-ca 0.30.2 as an SSH certificate authority, tested with OpenSSH 10.0. Why certificates beat authorized_keys and trust-on-first-use, switching the SSH CA on when step-ca is first set up, signing a host key (and the argument order that trips it), the two sshd_config lines and the single @cert-authority line in known_hosts, a 16-hour user certificate, four login tests including a wrong user and an untrusted host, renewing a host certificate with sshpop, and where it falls down.
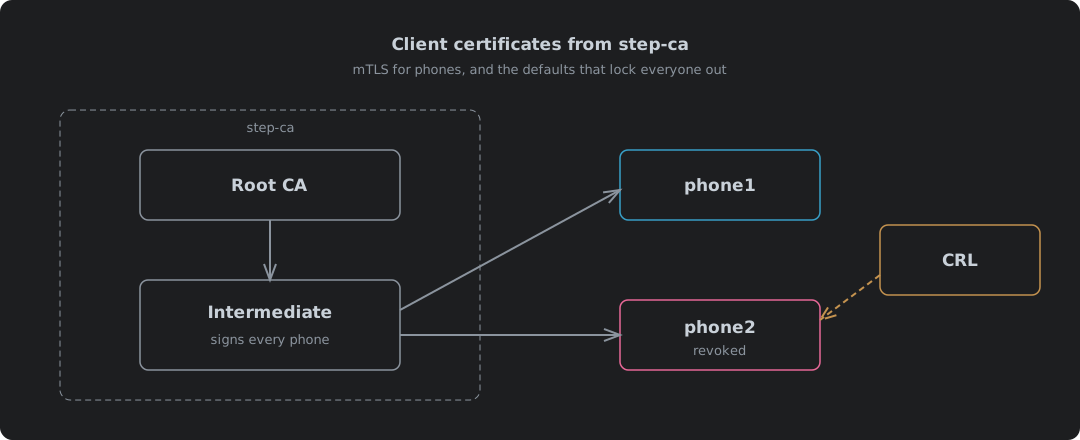
Client Certificates From step-ca, And The Defaults That Lock Everyone Out
Using step-ca 0.30.2 to issue client certificates for mutual TLS, tested end to end with nginx 1.30.5 and Caddy 2.11.7. Why phones are the hard case, raising the 24-hour certificate limit in ca.json, turning the CRL on, why it fails with “different CRL scope” until idpURL and a template add a matching distribution point, the root CRL nginx needs for the whole chain, publishing CRLs over plain HTTP on IPv4 and IPv6, the refresh job that stops an expired CRL locking everyone out, and issuing, packaging, installing and revoking a phone’s certificate.
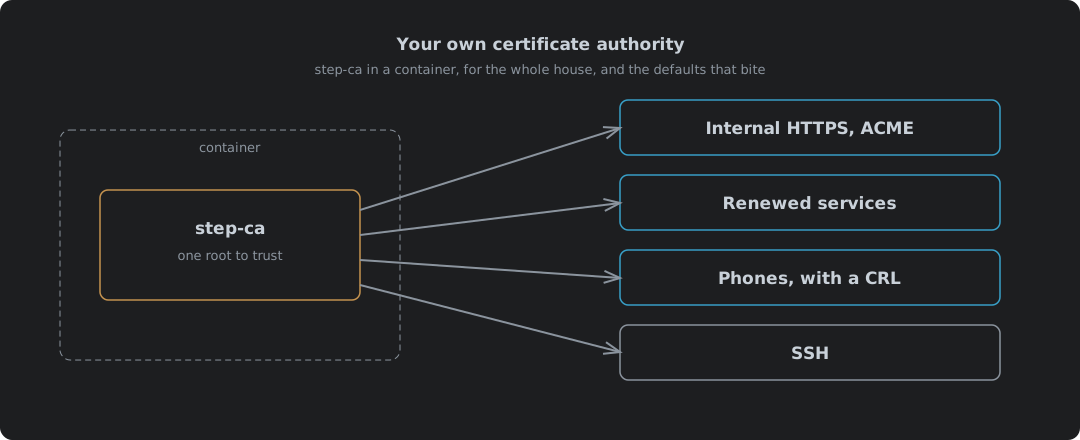
Your Own Certificate Authority: step-ca In A Container
Running Smallstep’s step-ca 0.30.2 in a Podman or Docker container as the certificate authority for everything inside the house, all of it tested. Why a private CA beats self-signed certificates and public ones for internal names, starting it with ACME and SSH switched on, the two passwords the image generates and where each one goes, trusting the root on every device, internal HTTPS for Caddy or anything else that speaks ACME, and step ca renew for services that do not. Client certificates and SSH each have their own post.
Webex Is Looking For Your Certificates On A Cisco Build Server
Webex 46.8.0.35631 on Fedora 44 sits behind a yellow banner reading “Offline - No internet connection” while every other program on the machine reaches the internet without complaint. It stopped the VoIP line dead. The network was never the problem: Cisco bundle their own fork of OpenSSL and built it with OPENSSLDIR set to /workspace/.conan2/p/b/cisco8ee8b59cf93de/p/ssl, a directory that exists on a build container and nowhere else, so it loads no trust anchors and every handshake fails. The post runs in order: what the broken state actually is, asking the shipped library where it thinks its certificates live, reproducing the exact error code outside Webex, why nothing warns you, the two fixes that do not work and why, and the one that does. Then the build process: they used $ORIGIN for the code and left three data paths absolute, the RPM header names a container ID so the container was already in the pipeline and never used to run the result, the package requires a glibc from 2018 because they will not link statically, 2.2 GB is shipped twice, and it carries no documentation and no file marked as configuration. Then how it should have been built, the six fixes and the one-line check that catches it. And finally the cross-check: Cisco hold 98 entries in CISA’s known-exploited catalogue, second only to Microsoft, and a trust path nobody checked and a bypass nobody checked are the same failure at different stakes.